
dart-casbin
An authorization library that supports access control models like ACL, RBAC, ABAC in Dart/Flutter

- Stars
- 44
- Forks
- 12
- Last push (UTC)
- May 15, 2026
- Project status
- Active
Original README
English project snapshot. Visit GitHub for the latest content.
dart-casbin


An authorization library that supports access control models like ACL, RBAC, ABAC in Dart.
News: Are you still worried about how to write the correct Casbin policy? Casbin online editor is coming to help! Try it at: http://casbin.org/editor/
Table of Contents
All the languages supported by Casbin:
 |
 |
 |
 |
|---|---|---|---|
| Casbin | jCasbin | node-Casbin | PHP-Casbin |
| production-ready | production-ready | production-ready | production-ready |
 |
 |
 |
 |
|---|---|---|---|
| PyCasbin | Casbin.NET | Casbin-CPP | Casbin-RS |
| production-ready | production-ready | beta-test | production-ready |
Supported models
- ACL (Access Control List)
- ACL with superuser
- ACL without users: especially useful for systems that don't have authentication or user log-ins.
- ACL without resources: some scenarios may target for a type of resources instead of an individual resource by using permissions like
write-article,read-log. It doesn't control the access to a specific article or log. - RBAC (Role-Based Access Control)
- RBAC with resource roles: both users and resources can have roles (or groups) at the same time.
- RBAC with domains/tenants: users can have different role sets for different domains/tenants.
- ABAC (Attribute-Based Access Control): syntax sugar like
resource.Ownercan be used to get the attribute for a resource. - RESTful: supports paths like
/res/*,/res/:idand HTTP methods likeGET,POST,PUT,DELETE. - Deny-override: both allow and deny authorizations are supported, deny overrides the allow.
- Priority: the policy rules can be prioritized like firewall rules.
How it works?
In Casbin, an access control model is abstracted into a CONF file based on the PERM metamodel (Policy, Effect, Request, Matchers). So switching or upgrading the authorization mechanism for a project is just as simple as modifying a configuration. You can customize your own access control model by combining the available models. For example, you can get RBAC roles and ABAC attributes together inside one model and share one set of policy rules.
The most basic and simplest model in Casbin is ACL. ACL's model CONF is:
# Request definition
[request_definition]
r = sub, obj, act

# Policy definition
[policy_definition]
p = sub, obj, act

# Policy effect
[policy_effect]
e = some(where (p.eft == allow))

# Matchers
[matchers]
m = r.sub == p.sub && r.obj == p.obj && r.act == p.act
An example policy for ACL model is like:
p, alice, data1, read
p, bob, data2, write
It means:
- alice can read data1
- bob can write data2
Features
What Casbin does:
- enforce the policy in the classic
{subject, object, action}form or a customized form as you defined, both allow and deny authorizations are supported. - handle the storage of the access control model and its policy.
- manage the role-user mappings and role-role mappings (aka role hierarchy in RBAC).
- support built-in superuser like
rootoradministrator. A superuser can do anything without explict permissions. - multiple built-in operators to support the rule matching. For example,
keyMatchcan map a resource key/foo/barto the pattern/foo*.
What Casbin does NOT do:
- authentication (aka verify
usernameandpasswordwhen a user logs in) - manage the list of users or roles. I believe it's more convenient for the project itself to manage these entities. Users usually have their passwords, and Casbin is not designed as a password container. However, Casbin stores the user-role mapping for the RBAC scenario.
Documentation
https://casbin.org/docs/overview
Online editor
You can also use the online editor (https://casbin.org/editor/) to write your Casbin model and policy in your web browser. It provides functionality such as syntax highlighting and code completion, just like an IDE for a programming language.
Tutorials
https://casbin.org/docs/tutorials
Installation
Add this to your package's pubspec.yaml file:
dependencies:
  casbin: ^1.0.0
Then run:
dart pub get
Or with Flutter:
flutter pub get
Get started
-
New a Casbin enforcer with a model file and a policy file:
import 'package:casbin/casbin.dart'; var e = Enforcer.fromModelPathAndPolicyFile('path/to/model.conf', 'path/to/policy.csv'); -
Add an enforcement hook into your code right before the access happens:
var sub = 'alice'; // the user that wants to access a resource. var obj = 'data1'; // the resource that is going to be accessed. var act = 'read'; // the operation that the user performs on the resource. if (e.enforce([sub, obj, act])){ // permit alice to read data1 } else { // deny the request, show an error } -
Besides the static policy file, Casbin also provides API for permission management at run-time. For example, You can get all the roles assigned to a user as below:
var roles = e.getRolesForUser(sub);
See Policy management APIs for more usage.
Policy management
Casbin provides two sets of APIs to manage permissions:
- Management API: the primitive API that provides full support for Casbin policy management.
- RBAC API: a more friendly API for RBAC. This API is a subset of Management API. The RBAC users could use this API to simplify the code.
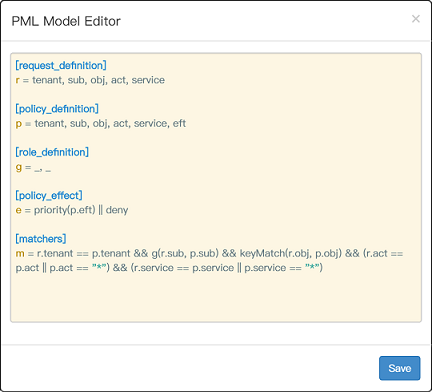
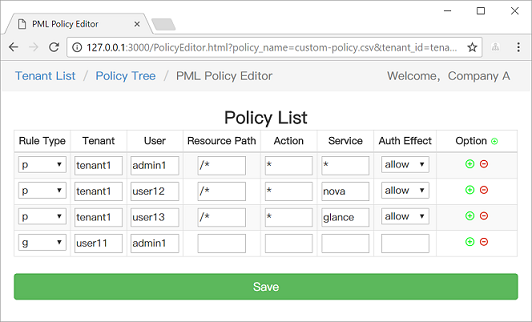
We also provide a web-based UI for model management and policy management:
Policy persistence
https://casbin.org/docs/adapters
Policy consistence between multiple nodes
https://casbin.org/docs/watchers
Role manager
https://casbin.org/docs/role-managers
Examples
| Model | Model file | Policy file |
|---|---|---|
| ACL | basic_model.conf | basic_policy.csv |
| ACL with superuser | basic_model_with_root.conf | basic_policy.csv |
| ACL without users | basic_model_without_users.conf | basic_policy_without_users.csv |
| ACL without resources | basic_model_without_resources.conf | basic_policy_without_resources.csv |
| RBAC | rbac_model.conf | rbac_policy.csv |
| RBAC with resource roles | rbac_model_with_resource_roles.conf | rbac_policy_with_resource_roles.csv |
| RBAC with domains/tenants | rbac_model_with_domains.conf | rbac_policy_with_domains.csv |
| ABAC | abac_model.conf | N/A |
| RESTful | keymatch_model.conf | keymatch_policy.csv |
| Deny-override | rbac_model_with_deny.conf | rbac_policy_with_deny.csv |
| Priority | priority_model.conf | priority_policy.csv |
Middlewares
Authz middlewares for web frameworks: https://casbin.org/docs/middlewares
Our adopters
https://casbin.org/docs/adopters
How to Contribute
Please read the contributing guide.
Star History
License
This project is licensed under the Apache 2.0 license.
Contact
If you have any issues or feature requests, please contact us. PR is welcomed.
- https://github.com/casbin/dart-casbin/issues
- https://discord.gg/S5UjpzGZjN

The Apache Software Foundation ↗
Categories
Dependencies used
Dependency list 5 items
- collection
^1.15.0 - expressions
^0.2.2 - quiver
^3.0.1 - lintsDevelopment
^5.1.0 - testDevelopment
^1.16.7
How do I choose a repository?
Start with your use case, compare repository activity, and check the original project before adopting it.
- Search by repository name, owner or description, then narrow the results by topic.
- Compare stars, forks and recent pushes. Stars show community interest, not a guarantee of quality.
- Read the README, license and issues on GitHub before using a project.
Sources and maintenance
“A repository is the most basic element of GitHub.”
GitHub Docs — About repositories ↗
- apache/casbin-dart-casbin · GitHub ↗
- GitHub Docs — Saving repositories with stars ↗
- Directory maintained by Ducafecat ↗